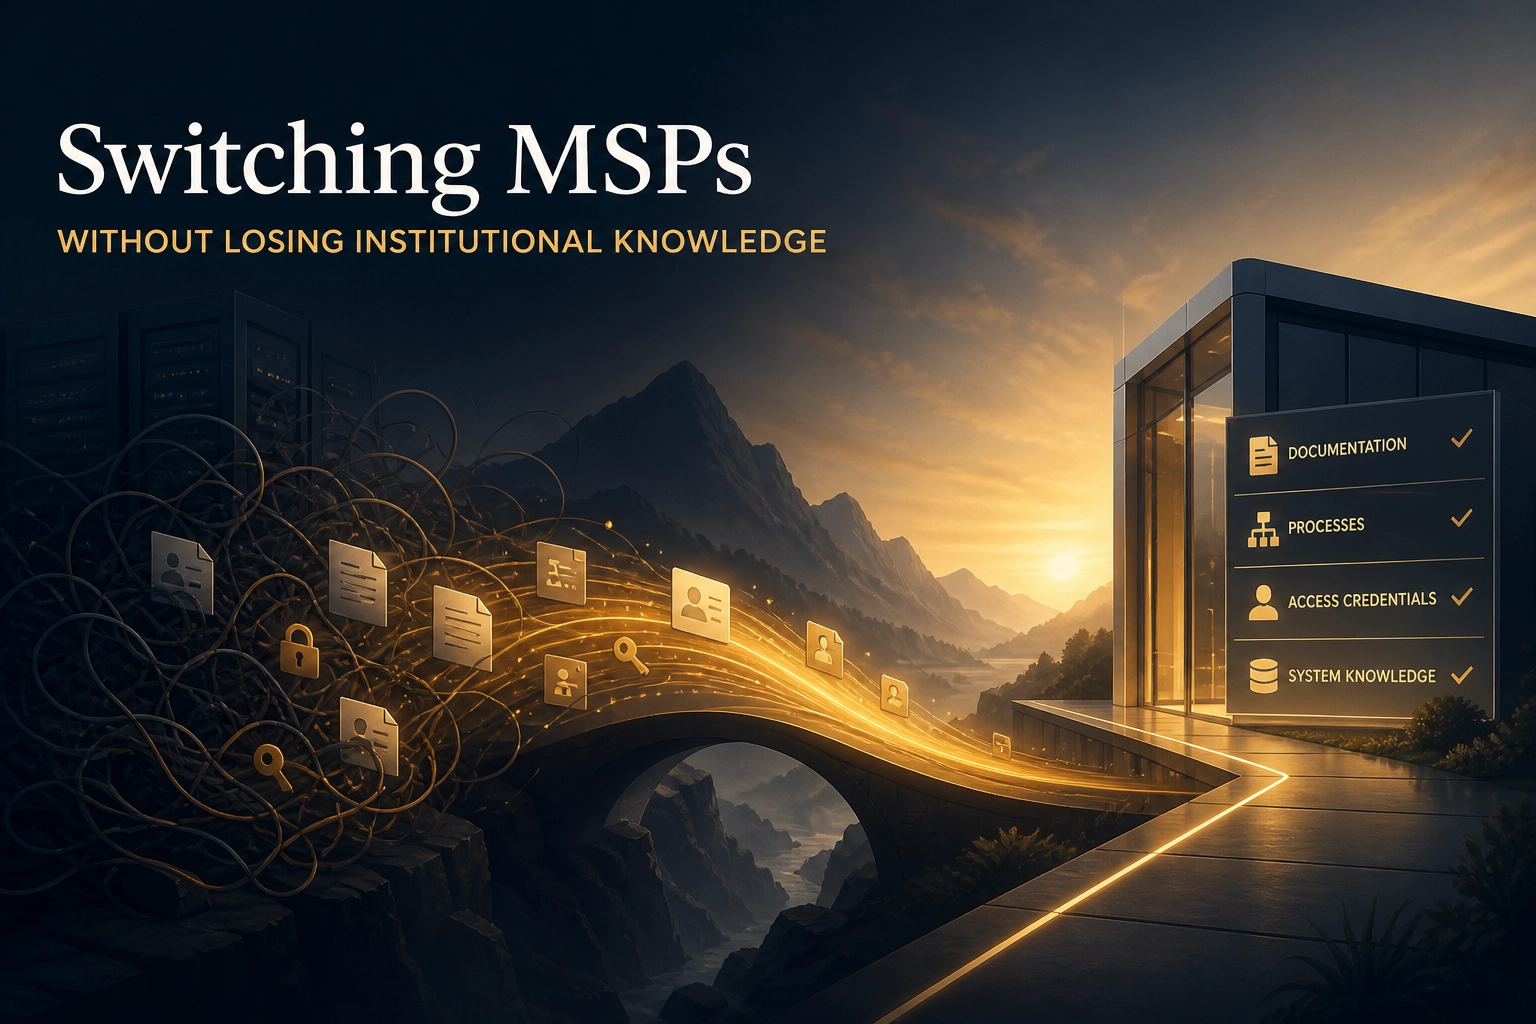
Switching managed it service provider is rarely a contract problem. It is a knowledge problem. The signature changes, the invoices reroute, and yet the finance close still depends on a script nobody documented. The admin credentials still sit with someone who has already moved on. The escalation contact for a critical vendor never made it into the new provider’s runbook. That is how a switch can reproduce the old provider’s blind spots instead of fixing them.
For businesses in Exton, Philadelphia, Wilmington, Cherry Hill, Lancaster, and Reading, the difference is a defined handover. The operational steps below draw on the author’s own transition experience, while the documented evidence base (Morais et al. on knowledge loss, NIST on authentication and account management, and the CISA-led advisory on MSP access) is academic and government guidance that does not cover provider switches specifically. This tutorial walks through the mechanics that matter after the fix-or-replace decision: credentials and admin access transfer, ticket history as archaeology, undocumented workarounds, vendor contacts and escalation paths, the written handover package, and the overlap period. You will learn what a managed IT service provider should hand over and how to build an overlap that lets the incoming provider inherit context instead of guessing. By the end, you will see why what a switch is worth is decided by the handover, not the contract.
Why a New Provider Reproduces the Old One’s Blind Spots
Provider switches get decided on service quality and priced on seats or devices. The transition plan that follows covers contract terms, notice periods, and billing cutover. It rarely covers the operational reasoning behind the configuration: why a firewall rule exists, why a script runs at 4am, why one department bypasses the ticketing system entirely. None of that lives in the contract.
Knowledge loss in provider transitions is a documented, recurring problem, and it does not stop repeating on its own. No study measures this, so treat the reproduction mechanism as a practitioner hypothesis to test, not a finding. Within a couple of business quarters, the incoming provider’s documentation starts to resemble the outgoing provider’s, because both were built from the same incomplete starting point.
The reproduction runs through gaps, not indifference. Handed an undocumented workaround, a new engineer guesses. The guess may match the old one or invent a different one, and either way it stays unwritten, so the next person inherits the same blank page. Keeping a repaired MSP relationship accountable is a separate discipline, and it does not recover what was never handed over.
The fix-or-replace decision draws the attention. The mechanics that follow determine whether the switch produces real improvement or a new logo on the same blind spots.
What a Managed IT Service Provider Actually Hands Over
A handover is not one document. It is several interdependent groups of items.
Contract. Notice period served, final invoice and true-up, equipment ownership, licenses held in the provider’s name, and account and tenant details for the platforms in use. Confirm who holds each subscription before you settle on which support model fits.
Control. Global and delegated admin accounts, emergency access credentials, MFA devices and recovery codes, domain registrar access, DNS control, backup consoles, and API keys tied to service accounts. A joint advisory from CISA and international partners describes MSPs as holding privileged access to and from customer systems, so inventory and rotate each one rather than forwarding it; the advisory does not prescribe a handover, but the exposure it describes argues for it.
Context. Ticket history with resolution notes, the process and workaround register, network and system diagrams, and the change log recording when things were altered and why. These items are not covered by published standards; treat them as this article’s recommendation.
Relationships. Named vendor account managers, support contract numbers, circuit IDs, warranty end dates, and the escalation sequence the incumbent actually used when something broke at 2am.
These groups are interdependent. A credential inventory without a workaround register tells the incoming team what it can log into but not what it will break by touching it.
Credentials and Admin Access: The Item Everyone Remembers, and Still Gets Wrong
The control items are the easy part. NIST SP 800-63B-4 defines authentication as establishing that a subject is in control of the secrets used to authenticate. The secrets are the asset, not the paperwork, so handing over a password hands over control.
That principle argues for rotation, not transfer: change every credential the outgoing provider touched and record the change, rather than pass it on with a note that the password is unchanged.
Repeat authentication gives reasonable risk-based assurance that today’s user is the same party who configured the service, and a provider switch breaks exactly that assumption. Re-verify instead of trusting inherited state.
Inventory before rotating, because rotation without a list always misses something: global and delegated admin roles, service accounts and API keys, MFA enrollments and recovery codes, domain registrar and DNS, backup and monitoring consoles, and the documentation platform itself.
The standard also separates the credential service provider, the verifier, and the relying party. Deciding who administers the secret store, who verifies access, and which systems depend on it gives the handover structure. It sets authentication principles, not an offboarding procedure, so treat it as a principle, not a checklist for a provider exit.
Sequence it as you would IT integration after an acquisition: one layer, then a gate.
Ticket History: Reading the Archaeology Instead of Starting Over
Once credentials are rotated, ticket history is the next asset to secure. Request the export while access still exists: a plain export with timestamps, categories, priorities, and resolution notes, tested to confirm it opens outside the outgoing provider’s platform. Portal access typically ends on the contract’s last day. Assume it will and export before then.
Then read it like archaeology. Hunt for volume clusters. One category generating repeat tickets across months signals either an unresolved root cause or a workaround someone reapplies by hand every time it fails. Read closure notes rather than subject lines, because “resolved” frequently means the user found a way around the problem, and that way around is what the incoming team must inherit.
Build a short list of the systems producing the most tickets, then annotate each with what the incumbent actually did. Not what the queue recorded as the category. Finally, flag tickets describing configuration changes with no matching documentation entry; those are the clearest map of what the handover package is missing. If you are still weighing a switch, these MSP scoring benchmarks turn frustration into documented evidence.
Undocumented Workarounds: The Finance Close That Runs on a Script Nobody Owns
Ticket history ends where this begins.
Consider a typical case: a finance close that depends on a scheduled export run by a script on a server nobody remembers building. The script drops a file into a shared mailbox; a controller picks it up. Skip one step and the close fails quietly.
Workarounds like this exist for ordinary reasons: a vendor limitation, an integration gap, a deadline that left no time for a proper fix. The exposure tends to surface at the first close after the switch, though no published study measures how often.
Capture method matters more than the template. Ask the outgoing team to walk each critical process on a recorded call, write the steps in sequence, and ask finance, payroll, and scheduling staff which workarounds they rely on. They often know the order of operations better than IT does.
Where a process feeds audited financial reporting, ask what the workaround leaves unlogged. This is a question to put to your auditors, not a rule the article can state. That script often runs on aging infrastructure with no refresh plan.
Vendor Contacts and Escalation Paths
Vendor relationships carry the same institutional weight. Before access ends, collect named account managers, support contract numbers, and portal logins for every vendor in the stack. A generic support queue restarts the relationship at tier one and discards the escalation history the incumbent built.
Record hardware and circuit identifiers: serial numbers, warranty end dates, circuit IDs, and license entitlements. These details turn a vendor call into same-day dispatch instead of a week of verification.
Document the escalation sequence as it was actually used. If the incumbent called a specific carrier engineer when an ISP circuit dropped, capture that name and the response time. Relationships transfer even when no document exists.
Then check which subscriptions sit in the outgoing provider’s tenant. Licenses bought through a provider may not transfer cleanly, so confirm which need migration or repurchase before the switch date. Buyers reopening MSP contracts can use the same register to sort transferable entitlements from locked ones.
Building the Handover Package: What Belongs in Writing
The vendor register only counts once the same document defines everything else that must change hands. Our recommendation: put the handover package in the termination or transition clause as a contractual deliverable. A handover requested as a favor in the final week delivers whatever happens to be findable.
It should contain: asset inventory with owners; credential inventory and rotation log; ticket export; process and workaround register; vendor register with contracts and contacts; current network and system diagrams; change log; and open risks with owners on both sides.
Every item needs acceptance criteria: a named owner, a stated format, a delivery date, and the person who confirms receipt. An item with no owner is an item that arrives late or not at all. Prefer evidence to promises: a rotation log with timestamps and a hash of the exported ticket file is stronger evidence than an email asserting credentials were changed. This is our recommendation, not a standard.
Write the outgoing provider’s obligations, the incoming provider’s intake review, and any payment holdback into the same managed service provider services agreement. Terms split across separate documents get negotiated separately, and the handover loses. The same discipline applies when vetting an IT advisory firm for the cleanup afterward.
The Overlap Period: What It Buys and How to Use It
Once the package is documented, the overlap period is what turns it into working context. Overlap is not a courtesy gesture. It is the only window in which the incoming team can ask why a firewall rule exists or why a script runs at 4 a.m. while the person who configured it is still reachable.
The length is a judgement call, not a benchmark: set it against your riskiest recurring processes rather than a round number. As a working recommendation, one full close and one full payroll cycle make a sensible floor.
Require a parallel run on one critical cycle, both teams executing the procedure independently before comparing outputs; the practice is standard guidance in our experience, though no source we can cite mandates it. Divergence surfaces undocumented steps faster than any interview.
Test escalation paths while both relationships still exist. Open a ticket with each major vendor through the new account relationship and confirm the path works before the old one closes. Carrying those relationships across is where vendor alignment by design genuinely begins.
Define the exit in advance: which access the outgoing provider retains during overlap, the date it is revoked, and who confirms revocation in writing. An open overlap with no end date is an open door.
How to Verify the Transfer Actually Happened
Once the overlap period closes, verification shifts from observation to testing. A signed checklist is not proof that knowledge changed hands.
Test instead of trusting. Ask the incoming team to restore from backup, execute the close procedure end to end, and resolve a synthetic ticket in each major platform, then review the results together.
Compare the new provider’s documentation against the handover package line by line and record every missing item. A useful heuristic: the gaps you find in week one are the incidents you avoid in month three.
Independently confirm that no outgoing-provider accounts, API keys, delegated admin roles, or MFA enrollments remain active. Written assurance is not verification, so check the identity and access consoles yourself.
Ask end users after a reasonable default of about 30 days. Staff who depended on an undocumented workaround will report breakage before monitoring or ticket volume does.
Where internal capacity is thin, an independent review of what actually transferred surfaces gaps before they become incidents. That is the kind of MSP relationship cleanup Orloff Phillips handles for businesses across Exton, Philadelphia, Wilmington, Cherry Hill, Lancaster, and Reading.
What a Switch Is Worth Is Decided by the Handover, Not the Contract
The signature changes who invoices you. The handover package changes what your business actually runs on, so judge the switch by the package. Ask whose documentation describes your business six months after the switch, and whether the people now supporting it can explain why the systems are configured the way they are. If the answers describe the old setup rather than a new understanding, nothing of value crossed the gap. Ninety days is our recommended test for the new managed IT service provider: not how fast the first month’s queue cleared, but whether the old blind spots reappeared in the new documentation.
Conclusion
A managed IT switch is only as strong as what crosses the gap, and the knowledge that transfers, not the signature collected, is what you are buying. Ninety days is our recommended test: not how fast the first queue cleared, but whether the old blind spots reappeared in the new documentation.
If internal capacity is thin, your next step is an independent review of what actually transferred. Orloff Phillips handles that MSP relationship cleanup for businesses across Exton, Philadelphia, Wilmington, Cherry Hill, Lancaster, and Reading. Judge the switch by the knowledge you kept, not the signature you collected.
Leave a Reply