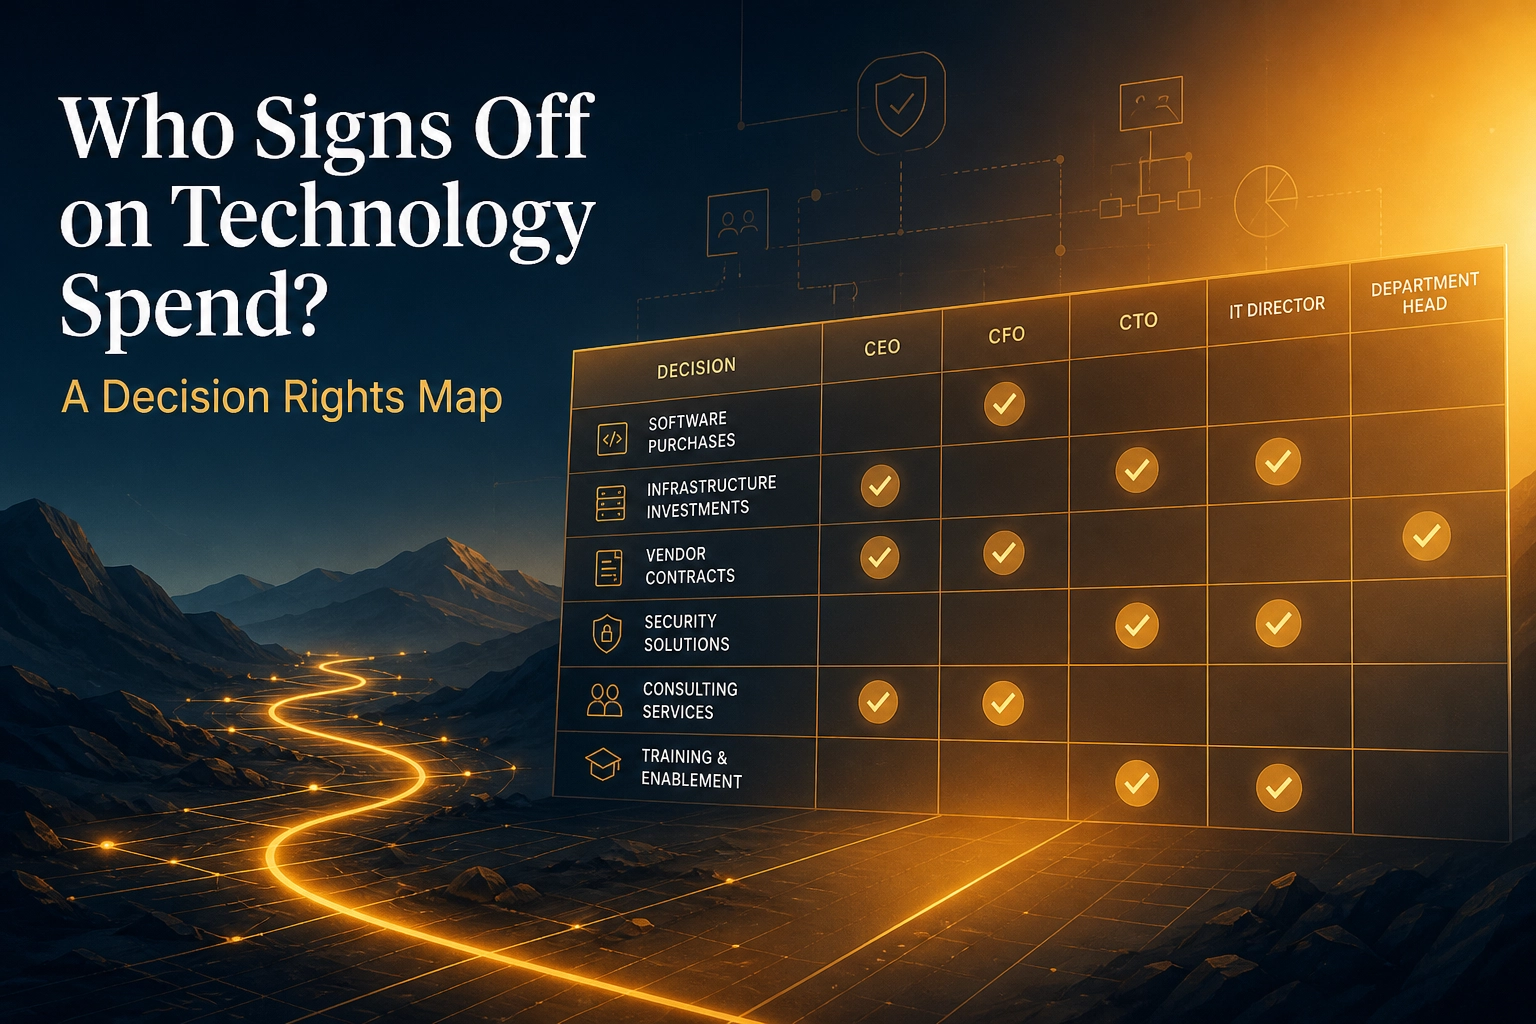
In most mid-market companies, nobody can answer a simple question: who approved this spend? Authority defaults to whoever is loudest in the room, or to whatever a provider’s renewal notice proposes. That is not IT governance. It is drift.
Decision rights are not a philosophy. They are an artifact you can draw: a threshold table showing who may commit, who must escalate, and the exact point where a provider’s recommendation stops being advice and becomes a commitment.
This analysis builds a practical map for teams around Exton, Philadelphia, Wilmington, Cherry Hill, Lancaster, and Reading PA. We will examine why governance defaults to volume; what decision rights actually mean in IT governance; four categories where technology commitment happens; and a threshold table covering capital purchases, contract changes, exceptions, and security waivers. We will also trace where a provider’s recommendation crosses into commitment, how escalation paths fail when a rung is empty, and how to adapt frameworks like COBIT without copying them.
By the end, you will have a table worth publishing, and a reason to make it stick.
Why IT Governance Defaults to Whoever Is Loudest in the Room
In most mid-market companies, “who can approve this?” is answered from memory, seniority, or volume, and it changes with whoever is in the room. That is observation, not survey data, and the fix is a document, not a culture program.
Two defaults fill the vacuum: volume, and the provider’s own timetable.
Unwritten authority costs money in three places: cycle time, every approval becomes a fresh negotiation; audit exposure, no evidence trail shows who accepted which risk; and pricing leverage, a provider sensing no one can commit paces the deal to its own convenience.
Governance is a design artifact, not a personality trait: it is the deliberate system of principles, decision models and accountability mechanisms an organization uses to decide where money goes and who answers for the outcome.
Operators across Exton, Philadelphia, Wilmington, Cherry Hill, Lancaster and Reading rarely resist delegating authority; they simply have not written the one-page document delegation requires, the same gap owning IT strategy without a CIO tends to expose.
What Decision Rights Actually Mean in IT Governance
A decision right is the named authority to commit a specific resource up to a specific limit, plus the obligation to escalate above it. Authority without a ceiling is a standing permission, and standing permissions accumulate unbudgeted spend.
Every row needs three answers: who may commit, at what threshold, and who must be informed afterward. Notification is not approval. Blur the two and approvals stall for a week waiting on someone whose only real role was to be told.
The scope of the table, then, is the slice of governance that governs spend: who may commit, how much, and who is told. The spend table is one slice, the one that shows up in contracts, invoices and renewal notices and often sits behind a fractional CIO engagement.
Separate accountable from consulted. Finance holds the budget, IT holds technical judgment, the MSP holds operational knowledge, but exactly one name per row signs. Committees can advise a signature, not be one.
Define vocabulary before setting numbers. “Security exception,” “change of scope” and “material change” mean different things to a CFO, a systems administrator and an account manager. A table that inherits that ambiguity just relocates the argument.
Four Categories Where Technology Commitment Actually Happens
With the vocabulary settled, commitment takes four distinct shapes.
Capital purchases
Hardware refresh, new seats, platform licenses and one-time implementation fees need their own band: lumpier amounts, longer useful life. Tie these to a funded refresh cycle, not the fiscal calendar.
Contract changes
Renewal uplift, term extensions, seat true-ups, scope additions and auto-renew clauses are where unbudgeted commitment most often hides, because the decision arrives disguised as an administrative formality.
Exceptions
The deviation from standard build, the department-level tool bought outside the roadmap, the integration delivered ahead of architecture review. Each is a commitment, because someone must support it later.
Security waivers
Accepting a known risk, deferring a control or granting a policy exception binds the business to a risk it may never have priced. Authority to grant one should sit higher than authority to run the control.
Below a stated noise floor, routine operating spend sits with one owner and requires no approval. A table that gates everything collapses under its own weight, discrediting the rows that mattered.
A Threshold Table for Technology Spend Authority
With the four categories named, each now needs a row and a ceiling. Build it as a five-column table: commitment category, the role that may commit, that role’s escalation ceiling, the evidence required to close the decision, and who must be notified. The bands below are illustrative, offered to show shape rather than prescription. Calibrate against your own operating budget: up to $5,000 commits with the department head; $5,001 to $25,000 with the IT director, notifying Finance; $25,001 to $100,000 with the CFO on CIO sign-off; above $100,000 with the CEO or board.
Security waivers need a different grid. Money is the wrong axis: a zero-dollar waiver deferring multi-factor authentication on a finance system outweighs a $30,000 laptop refresh. Escalate waivers on risk class, not price.
Date the document and name an owner. An undated table drifts out of alignment before long, and one stale row discredits the rest. Publish it where your provider can see it. The table instructs your MSP as much as it controls you, and requires the governance cadence that keeps it alive after the first revision.
Row One: Capital Purchases and One-Time Commitments
Capital purchases are their own row. If hardware turns over on a four-year cadence, the table states how that cycle is funded and who reopens it when a device dies in year two; a dependency-ordered rollout plan keeps that sequencing honest.
Anything above the middle band needs a named business sponsor, not just an IT requester. Capital without an operational owner becomes shelfware, and shelfware is the fastest way to lose executive trust in the table.
Tie quoting discipline to the threshold: three comparable quotes above a set figure, one quote below it. Paperwork stays proportional to the amount at risk.
Expire the approval. A quote accepted nine months after sign-off is a new decision, so send anything older than a stated window back through the table without apology.
The same logic governs what happens once the purchase becomes a subscription.
Row Two: Contract Changes and Renewals
Renewal uplift, auto-renew and term extension are commitments, not paperwork. Give the provider’s notice a mandatory landing point in the table: a named recipient and an internal deadline set well ahead of the contractual one. Run a 90-day internal clock rather than the notice period the provider sets. A table that activates only when the notice arrives has already conceded the negotiation.
Classify any change the provider requests after signature as a new decision, not an amendment to the original. That single rule stops scope accumulating one small addendum at a time. Seat true-ups and consumption overages deserve their own band: monthly, headcount-driven, rarely worth executive sign-off below a set number, yet never invisible to Finance.
If renewals keep landing as settled facts, benchmark your MSP before the next one arrives.
Row Three: Exceptions and Security Waivers
Exceptions and waivers are where a threshold table earns its keep, because the commitment is risk rather than dollars.
Record every security waiver as a risk acceptance with three mandatory fields: the specific risk being accepted, an expiry date, and a business owner who does not operate the control. A waiver without an expiry date is a permanent policy change granted by accident.
Anchor the row to a written risk appetite statement. Without that anchor, the waiver process simply formalizes drift that already happened. Waivers are commitments because someone must support the exception long after the requester has moved on.
Prohibit self-approval. The role operating a control should never grant the exception to it, however sensible the exception looks.
Borrow framework language rather than inventing a bespoke register. COBIT 2019 governance objectives and the evaluate, direct and monitor cycle in ISO/IEC 38500 supply defensible wording for a waiver register that auditors and providers both recognize.
Where a Provider’s Recommendation Stops Being Advice
The boundary is a signature, not a tone. A recommendation becomes a commitment the moment someone holding the right to commit accepts it in writing, or the moment a renewal clause accepts it silently on the customer’s behalf.
Three tells that advice has already become a commitment: the scope now appears in a statement of work, the charge appears on a recurring invoice, or the work has moved into the ticket queue as business as usual.
Providers fill ambiguity rationally. An MSP with no named approver defaults to the highest-ranking person who responds, then treats that response as standing authority for the next renewal. That is how two years of scope can arrive without a single formal decision.
Publish the boundary outward. Give the provider the named approver per category, the thresholds, and a response expectation, and require written acknowledgment in the contract’s governance section or the SOW.
Keep recommendation intake separate from approval. An MSP should be free to propose and should never accept its own proposal, even a good one. If you are still vetting an advisory firm, confirm the proposal-and-approval split before signing.
Escalation Paths and the Cost of an Empty Rung
In IT governance, publishing the boundary exposes a new failure mode: the empty rung. Name a backup for every approver. A single named approver is a single point of failure, and a provider that learns the approver is unreachable will route the decision around them permanently. Time-box escalation: state that an unanswered request moves up one rung after a defined period, and make the clock visible to the requester, not only the approver. Clarify that escalation is not re-approval. It moves authority up a level; it does not restart the request. Writing this down removes the most common excuse for a stalled cycle. Log declines and deferrals, not just approvals. A register of what was turned down and why is the fastest input to the next vendor negotiation, and it protects the person who said no. Measure the table quarterly with three numbers: cycle time per request, share of spend that escalated, and count of waivers granted with their expiry dates. Bands that never trigger an escalation are set too high. Choosing the right backup often depends on what your team can own.
Adapting IT Governance Frameworks Without Copying One
Once the bands and escalation clocks are set, the last question is where the model comes from. Governance frameworks reward adaptation rather than wholesale adoption: they are not plug-and-play, and governance is not one-size-fits-all. COBIT, ISO/IEC 38500, ITIL and architecture review are candidates to adapt, never templates to take as given.
COBIT 2019, the current edition, is ISACA’s business framework for governing enterprise IT, described by ISACA as helping IT professionals and enterprise leaders fulfill their governance and management responsibilities. (ISACA’s figure of 95,000 constituents in 160 countries dates to a 2012 publication, not today.) ITIL supplies the change and exception vocabulary that makes the exception row legible to operations, and architecture review supplies the gate that stops exceptions from bypassing design standards.
Orloff Phillips works with mid-market firms to clean up MSP relationships, and the first practical step is usually converting an unwritten approval habit into a published table. Keep it to one page with one owner. A framework-shaped document nobody can locate is worse than the habit it replaced: it adds ceremony without adding a decision.
Conclusion: Publish the Table and Make It Stick
The framework decision is settled, so the remaining work is publication. Draft version one this month with the four categories and four bands, label it clearly as a draft, and circulate it to Finance, IT and your provider on the same day.
A row without a backup name is not finished.
Send the table to your MSP with a written request for acknowledgment and a named counterpart who receives proposals. Wait for that confirmation before the next renewal notice arrives, so the provider meets the table before the deadline does.
Add a review date and a waiver register with owners and expiry dates. Re-run the bands at your next renewal cycle, cut any band that never triggered an escalation, and publish version two. Let the document change as the business does.
Leave a Reply